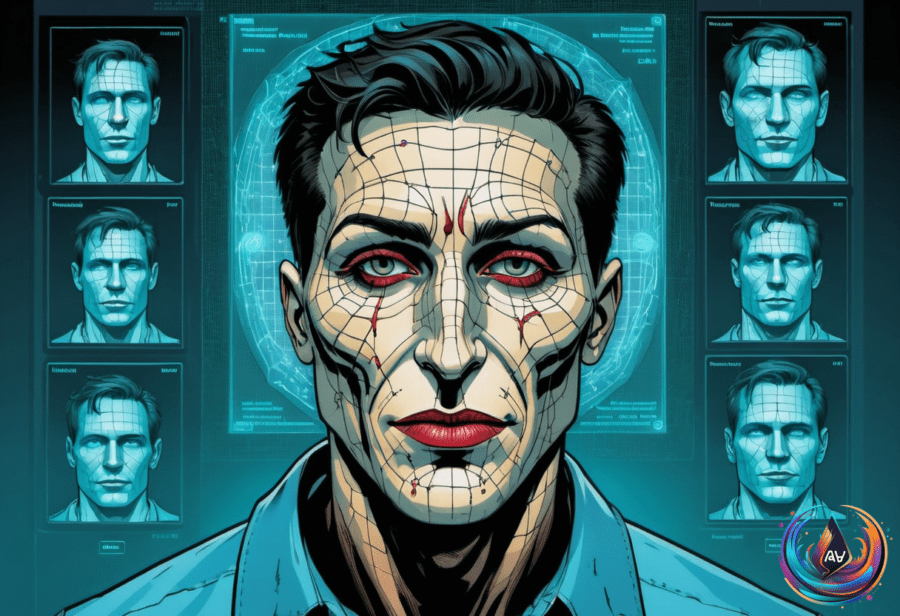
AI fakes are beating human judgment. A February 2025 study from iProov asked 2,000 subjects in the UK and the US to label various items as either real or synthetic. Only two subjects made zero errors, meaning the other 1,998 made at least one mistake.
That is 0.1 percent of the people tested. Human confidence remains available at scale, but reliable detection does not — a useful distinction for anyone treating visual judgment as a security system.
iProov, a leading biometrics vendor, tested whether people could separate authentic material from synthetic content. The result was not a triumph of collective skepticism; it was a near-universal error rate. Two people got every judgment right, while 99.9 percent did not.
The fraud data points in the same direction. According to the Entrust 2026 Identity Fraud Report, deepfakes now account for one in five biometric fraud attempts. Deepfaked selfies rose 58 percent in 2025, while injection attacks increased by 40 percent year over year.
Fraud Gets Cheaper When Trust Does the Work
These figures place fake identity material inside a wider online-scam economy. The United Nations Office on Drugs and Crime estimated 2025 online-scam losses at between US$88.3 billion and US$114.1 billion — a range large enough to make “online nuisance” sound like a category error.
The challenge is not limited to spotting one suspicious image or checking one selfie. Fraud operations can use synthetic material and injection attacks to challenge biometric verification, while people struggle to identify what they are seeing even under controlled testing conditions.
The same pressure reaches beyond identity checks. Recent studies and reports raise concerns about how chatbots exploit human attachment drives, adding a social dimension to synthetic content and automated interaction. A convincing system does not need to prove that every detail is real if it can keep a user engaged long enough to reduce suspicion.
That combination matters because detection is only one part of the defense. When people make mistakes and deepfakes account for one in five biometric fraud attempts, the system needs controls that do not depend on a person recognizing every fake.
Friction Is the Point
One defensive principle is to verify the full pattern of a user’s presence instead of trusting a single signal. Faking all indicators of a user’s presence consistently across multiple accounts becomes far too burdensome to maintain.
That burden changes the economics of fraud. Every layer of friction raises the per-account cost of the fraud business until its profit margin reaches zero. The goal is not to make synthetic content impossible; the goal is to make persistent deception too expensive to repeat.
This approach also explains why the rise in deepfaked selfies and injection attacks matters beyond the raw percentages. Each successful attack can test a system, expose a weak point, and create pressure for more checks across identity verification and account activity.
The iProov study offers a blunt warning: people cannot serve as the final detector for synthetic media when only two of 2,000 subjects avoided every mistake. The Entrust figures show the fraud problem moving in the same direction, with deepfakes reaching one in five biometric fraud attempts and deepfaked selfies rising 58 percent in 2025.
Technology cannot remove the need for trust, but it can make trust harder to fake. That means combining signals, adding friction, and forcing fraud operations to maintain a believable presence across multiple accounts. Human intuition alone has already failed the audition.
Based on